7 Common Pitfalls When Adopting Zero Trust Security

Zero Trust security is rapidly transforming the cybersecurity landscape. It moves away from traditional perimeter-based security models. In this approach, every connection attempt is continuously verified before granting resource access.

56% of global organizations say adopting Zero Trust is a “Top” or “High” priority.

This approach offers significant security advantages. But the transition process presents several potential pitfalls. Running into these can harm a company’s cybersecurity efforts.

Below, we’ll explore these common roadblocks. We’ll also offer guidance on navigating a successful Zero Trust security adoption journey.

Remembering the Basics: What is Zero Trust Security?

Zero Trust throws out the old “castle and moat” security model. The one where everyone inside the network perimeter is trusted. Instead, it assumes everyone and everything is a potential threat. This is true even for users already inside the network. This may sound extreme, but it enforces a rigorous “verify first, access later” approach.

Here are the key pillars of Zero Trust:

  • Least Privilege: Users only get access to the specific resources they need to do their jobs, no more.
  • Continuous Verification: Authentication doesn’t happen once. It’s an ongoing process. Users and devices are constantly re-evaluated for access rights.
  • Micro-Segmentation: IT divides the network into smaller segments. This limits the damage if a breach occurs.

Common Zero Trust Adoption Mistakes

Zero Trust isn’t a magic solution you can simply buy and deploy. Here are some missteps to avoid:

Treating Zero Trust as a Product, Not a Strategy

Some vendors might make Zero Trust sound like a product they can sell you. Don’t be fooled! It is a security philosophy that requires a cultural shift within your organization.

There are many approaches and tools used in a Zero Trust strategy. These include tools like multi-factor authentication (MFA) and advanced threat detection and response.

Focus Only on Technical Controls

Technology indeed plays a crucial role in Zero Trust. But its success hinges on people and processes too. Train your employees on the new security culture and update access control policies. The human element is an important one in any cybersecurity strategy.

Overcomplicating the Process

Don’t try to tackle everything at once. This can be overwhelming, and smaller companies may give up. Start with a pilot program focusing on critical areas. Then, gradually expand your Zero Trust deployment bit by bit.

Neglecting User Experience

Zero Trust shouldn’t create excessive hurdles for legitimate users. Adopting controls like MFA can backfire if employees aren’t involved. Find the right balance between security and a smooth user experience. Use change management to help ease the transition process.

Skipping the Inventory

You can’t secure what you don’t know exists. Catalog all your devices, users, and applications before deploying Zero Trust. This helps identify potential access risks. It also provides a roadmap for prioritizing your efforts.

Forgetting Legacy Systems

Don’t leave older systems unprotected during your Zero Trust transition. Integrate them into your security framework or consider secure migration plans. Forgotten legacy systems can lead to data breaches that impact your entire network.

Ignoring Third-Party Access

Third-party vendors can be a security weak point. Clearly define access controls and check their activity within your network. Set time-limited access as appropriate.

Remember, Zero Trust is a Journey

Building a robust Zero Trust environment takes time and effort. Here’s how to stay on track:

  • Set Realistic Goals: Don’t expect overnight success. Define achievable milestones and celebrate progress along the way.
  • Embrace Continuous Monitoring: Security threats are constantly evolving. Continuously watch your Zero Trust system and adjust your strategies as needed.
  • Invest in Employee Training: Empower your employees as active participants in your Zero Trust journey. Regular security awareness training is vital.

The Rewards of a Secure Future

Avoid these common mistakes and adopt a strategic approach. This will enable your business to leverage the big advantages of Zero Trust security. Here’s what you can expect:

  • Enhanced Data Protection: Zero Trust minimizes the damage from a potential breach. It does this by limiting access to sensitive data.
  • Improved User Experience: Streamlined access controls create a smoother experience for authorized users.
  • Increased Compliance: Zero Trust aligns with many industry regulations and compliance standards.

Are you ready to take the first step with Zero Trust security? Equip yourself with knowledge, plan your approach, and avoid these common pitfalls. This will enable you to transform your security posture as well as build a more resilient business in the face of evolving cyber threats.

Schedule a Zero Trust Cybersecurity Assessment

Zero Trust is quickly becoming a security expectation around the world. Our team of cybersecurity experts can help you get started deploying it successfully. Deploying it is a continuous journey towards a more secure future. We’re happy to be your trusted guides.

Contact us today to schedule a cybersecurity assessment to get started.

—
Featured Image Credit

This Article has been Republished with Permission from .
Here Are 5 Data Security Trends to Prepare for in 2024

With cyber threats evolving at an alarming pace, staying ahead of the curve is crucial. It’s a must for safeguarding sensitive information. Data security threats are becoming more sophisticated and prevalent. The landscape must change to keep up. In 2024, we can expect exciting developments alongside persistent challenges.

Over 70% of business professionals say their data privacy efforts are worth it. And that their business receives “significant” or “very significant” benefits from those efforts.

Staying informed about these trends is crucial. This is true whether you’re an individual or a business safeguarding valuable data.

Here are some key areas to watch.

1. The Rise of the Machines: AI and Machine Learning in Security

Artificial intelligence (AI) and machine learning (ML) are no longer futuristic concepts. They are actively shaping the cybersecurity landscape. This year, we’ll likely see a further rise in their application:

  • Enhanced Threat Detection: AI and ML algorithms excel at analyzing massive datasets. This enables them to identify patterns and anomalies that might escape human notice. This translates to a quicker detection of and reaction to potential cyber threats.
  • Predictive Analytics: AI can predict potential vulnerabilities and suggest proactive measures. It does this by analyzing past cyberattacks and security incidents.
  • Automated Response: AI can go beyond detection and analysis. Professionals can program it to automatically isolate compromised systems. As well as block malicious activity and trigger incident response procedures. This saves valuable time and reduces the potential impact of attacks.

AI and ML offer significant benefits. But it’s important to remember they are tools, not magic solutions. Deploying them effectively requires skilled professionals. Experts who can interpret the data and make informed decisions.

2. Battling the Ever-Evolving Threat: Ransomware

Ransomware is malicious software that encrypts data and demands a ransom for decryption. It has been a persistent threat for years. Unfortunately, it’s not going anywhere in 2024. Hackers are constantly refining their tactics, targeting individuals and businesses alike. Here’s what to expect:

  • More Targeted Attacks: Hackers will likely focus on meticulously selecting high-value targets. Such as critical infrastructure or businesses with sensitive data. They do this to maximize their impact and potential payout.
  • Ransomware-as-a-Service (RaaS): This enables those with limited technical expertise to rent ransomware tools. This makes it easier for a wider range of actors to launch attacks.
  • Double Extortion: Besides encrypting data, attackers might steal it beforehand. They then may threaten to leak it publicly if the ransom isn’t paid, adding pressure on victims.

3. Shifting Strategies: Earlier Data Governance and Security Action

Traditionally, companies have deployed data security measures later in the data lifecycle. For example, after data has been stored or analyzed. But a new approach towards earlier action is gaining traction in 2024. This means:

  • Embedding Security Early On: Organizations are no longer waiting until the end. Instead, they will integrate data controls and measures at the start of the data journey. This could involve setting data classification levels. As well as putting in place access restrictions. They will also be defining data retention policies early in the process.
  • Cloud-Centric Security: More organizations are moving towards cloud storage and processing. As they do this, security solutions will be closely integrated with cloud platforms. This ensures consistent security throughout the entire data lifecycle.
  • Compliance Focus: Data privacy regulations like GDPR and CCPA are becoming increasingly stringent. As this happens, companies will need to focus on data governance to ensure compliance.

4. Building a Fortress: Zero Trust Security and Multi-Factor Authentication

We’re in a world where traditional perimeter defenses are constantly breached. This is why the “Zero Trust” approach is gaining prominence. This security model assumes that no user or device is inherently trustworthy. Users and programs need access verification for every interaction. Here’s how it works:

  • Continuous Verification: Every access request will be rigorously scrutinized. This is regardless of its origin (inside or outside the network). Systems base verification on factors like user identity, device, location, and requested resources.
  • Least Privilege Access: Companies grant users the lowest access level needed to perform their tasks. This minimizes the potential damage if hackers compromise their credentials
  • Multi-Factor Authentication (MFA): MFA adds an important extra layer of security. It requires users to provide extra factors beyond their password.

5. When Things Get Personal: Biometric Data Protection

Biometrics include facial recognition, fingerprints, and voice patterns. They are becoming an increasingly popular form of authentication. But this also raises concerns about the potential for misuse and privacy violations:

  • Secure Storage Is Key: Companies need to store and secure biometric data. This is ideally in encrypted form to prevent unauthorized access or breaches.
  • Strict Regulation: Expect governments to install stricter regulations. These will be around the collection, use, and retention of biometric data. Organizations will need to ensure they adhere to evolving standards. They should also focus on transparency and user consent.

How to Prepare for Evolving Data Security Trends

Feeling a bit overwhelmed? Don’t worry, here are some practical steps you and your organization can take:

  • Stay Informed
  • Invest in Training
  • Review Security Policies
  • Embrace Security Technologies
  • Test Your Systems

Schedule a Data Security Assessment Today!

The data security landscape of 2024 promises to be both intriguing and challenging. We can help you navigate this evolving terrain with confidence.

A data security assessment is a great place to start. Contact us today to schedule yours.

—
Featured Image Credit

This Article has been Republished with Permission from The Technology Press.

Google & Yahoo’s New DMARC Policy Shows Why Businesses Need Email Authentication… Now

Have you been hearing more about email authentication lately? There is a reason for that. It’s the prevalence of phishing as a major security threat. Phishing continues as the main cause of data breaches and security incidents. This has been the case for many years.

A major shift in the email landscape is happening. The reason is to combat phishing scams. Email authentication is becoming a requirement for email service providers. It’s crucial to your online presence and communication to pay attention to this shift.

Google and Yahoo are two of the world’s largest email providers. They have implemented a new DMARC policy that took effect in February 2024. This policy essentially makes email authentication essential. It’s targeted at businesses sending emails through Gmail and Yahoo Mail.

But what’s DMARC, and why is it suddenly so important? Don’t worry, we’ve got you covered. Let’s dive into the world of email authentication. We’ll help you understand why it’s more critical than ever for your business.

The Email Spoofing Problem

Imagine receiving an email seemingly from your bank. It requests urgent action. You click a link, enter your details, and boom – your information is compromised.

The common name for this is email spoofing. It’s where scammers disguise their email addresses. They try to appear as legitimate individuals or organizations. Scammers spoof a business’s email address. Then they email customers and vendors pretending to be that business.

These deceptive tactics can have devastating consequences on companies. These include:

  • Financial losses
  • Reputational damage
  • Data breaches
  • Loss of future business

Unfortunately, email spoofing is a growing problem. It makes email authentication a critical defense measure.

What is Email Authentication?

Email authentication is a way of verifying that your email is legitimate. This includes verifying the server sending the email. It also includes reporting back unauthorized uses of a company domain.

Email authentication uses three key protocols, and each has a specific job:

  • SPF (Sender Policy Framework): Records the IP addresses authorized to send email for a domain.
  • DKIM (DomainKeys Identified Mail): Allows domain owners to digitally “sign” emails, verifying legitimacy.
  • DMARC (Domain-based Message Authentication, Reporting, and Conformance): Gives instructions to a receiving email server. Including, what to do with the results of an SPF and DKIM check. It also alerts domain owners that their domain is being spoofed.

SPF and DKIM are protective steps. DMARC provides information critical to security enforcement. It helps keep scammers from using your domain name in spoofing attempts.

Here’s how it works:

  1. You set up a DMARC record in your domain server settings. This record informs email receivers (like Google and Yahoo). It tells them the IP addresses authorized to send emails on your behalf.
  2. What happens next? Your sent email arrives at the receiver’s mail server. It is looking to see if the email is from an authorized sender.
  3. Based on your DMARC policy, the receiver can take action. This includes delivery, rejection, or quarantine.
  4. You get reporting back from the DMARC authentication. The reports let you know if your business email is being delivered. It also tells you if scammers are spoofing your domain.

Why Google & Yahoo’s New DMARC Policy Matters

Both Google and Yahoo have offered some level of spam filtering. But didn’t strictly enforce DMARC policies. The new DMARC policy raises the bar on email security.

  • Starting in February 2024, the new rule took place. Businesses sending over 5,000 emails daily must have DMARC implemented.
  • Both companies also have policies for those sending fewer emails. These relate to SPF and DKIM authentication.

Look for email authentication requirements to continue. You need to pay attention to ensure the smooth delivery of your business email.

The Benefits of Implementing DMARC:

Implementing DMARC isn’t just about complying with new policies. It offers a range of benefits for your business:

  • Protects your brand reputation: DMARC helps prevent email spoofing scams. These scams could damage your brand image and customer trust.
  • Improves email deliverability: Proper authentication ensures delivery. Your legitimate emails reach recipients’ inboxes instead of spam folders.
  • Provides valuable insights: DMARC reports offer detailed information. They give visibility into how different receivers are handling your emails. As well as help you identify potential issues. They also improve your email security posture.

Taking Action: How to Put DMARC in Place

Implementing DMARC is crucial now. This is especially true considering the rising email security concerns with email spoofing. Here’s how to get started:

  • Understand your DMARC options
  • Consult your IT team or IT security provider
  • Track and adjust regularly

Need Help with Email Authentication & DMARC Monitoring?

DMARC is just one piece of the email security puzzle. It’s important to put email authentication in place. This is one of many security measures required in the modern digital environment. Need help putting these protocols in place? Just let us know.

Contact us today to schedule a chat.

—
Featured Image Credit

This Article has been Republished with Permission from The Technology Press.

Beware of Deepfakes! Learn How to Spot the Different Types

Have you ever seen a video of your favorite celebrity saying something outrageous? Then later, you find out it was completely fabricated? Or perhaps you’ve received an urgent email seemingly from your boss. But something felt off.

Welcome to the world of deepfakes. This is a rapidly evolving technology that uses artificial intelligence (AI). It does this to create synthetic media, often in the form of videos or audio recordings. They can appear real but are actually manipulated.

People can use deepfakes for creative purposes. Such as satire or entertainment. But their potential for misuse is concerning. Deepfakes have already made it into political campaigns. In 2024, a fake robocall mimicked the voice of a candidate. Scammers wanted to fool people into believing they said something they never said.

Bad actors can use deepfakes to spread misinformation. As well as damage reputations and even manipulate financial markets. They are also used in phishing attacks. Knowing how to identify different types of deepfakes is crucial in today’s world.

So, what are the different types of deepfakes, and how can you spot them?

Face-Swapping Deepfakes

This is the most common type. Here the face of one person is seamlessly superimposed onto another’s body in a video. These can be quite convincing, especially with high-quality footage and sophisticated AI algorithms.

Here’s how to spot them:

  • Look for inconsistencies: Pay close attention to lighting, skin tones, and facial expressions. Do they appear natural and consistent throughout the video? Look for subtle glitches. Such as hair not moving realistically. Or slight misalignments around the face and neck.
  • Check the source: Where did you encounter the video? Was it on a reputable news site or a random social media page? Be cautious of unverified sources and unknown channels.
  • Listen closely: Does the voice sound natural? Does it match the person’s typical speech patterns? Incongruences in voice tone, pitch, or accent can be giveaways.

Deepfake Audio

This type involves generating synthetic voice recordings. They mimic a specific person’s speech patterns and intonations. Scammers can use these to create fake audio messages. As well as make it seem like someone said something they didn’t.

Here’s how to spot them:

  • Focus on the audio quality: Deepfake audio can sound slightly robotic or unnatural. This is especially true when compared to genuine recordings of the same person. Pay attention to unusual pauses. As well as inconsistent pronunciation or a strange emphasis.
  • Compare the content: Does the content of the audio message align with what the person would say? Or within the context in which it’s presented? Consider if the content seems out of character or contradicts known facts.
  • Seek verification: Is there any independent evidence to support the claims made? If not, approach it with healthy skepticism.

Text-Based Deepfakes

This is an emerging type of deepfake. It uses AI to generate written content. Such as social media posts, articles, or emails. They mimic the writing style of a specific person or publication. These can be particularly dangerous. Scammers can use these to spread misinformation or impersonate someone online.

Here’s how to spot them:

  • Read critically: Pay attention to the writing style, vocabulary, and tone. Does it match the way the person or publication typically writes? Look for unusual phrasing, grammatical errors, or inconsistencies in tone.
  • Check factual accuracy: Verify the information presented in the text against reliable sources. Don’t rely solely on the content itself for confirmation.
  • Be wary of emotional triggers: Be cautious of content that evokes strong emotions. Such as fear, anger, or outrage. Scammers may be using these to manipulate your judgment.

Deepfake Videos with Object Manipulation

This type goes beyond faces and voices. It uses AI to manipulate objects within real video footage. Such as changing their appearance or behavior. Bad actors may be using this to fabricate events or alter visual evidence.

Here’s how to spot them:

  • Observe physics and movement: Pay attention to how objects move in the video. Does their motion appear natural and consistent with the laws of physics? Look for unnatural movement patterns. As well as sudden changes in object size, or inconsistencies in lighting and shadows.
  • Seek original footage: If possible, try to find the original source of the video footage. This can help you compare it to the manipulated version and identify alterations.

Staying vigilant and applying critical thinking are crucial in the age of deepfakes.

Familiarize yourself with the different types. Learn to recognize potential red flags. Verify information through reliable sources. These actions will help you become more informed and secure.

Get a Device Security Checkup

Criminals are using deepfakes for phishing. Just by clicking on one, you may have downloaded a virus. A device security checkup can give you peace of mind. We’ll take a look for any potential threats and remove them.

Contact us today to learn more.

—
Featured Image Credit

This Article has been Republished with Permission from The Technology Press.

How to Organize Your Cybersecurity Strategy into Left and Right of Boom

In the pulsating digital landscape, every click and keystroke echoes through cyberspace. The battle for data security rages on. Businesses stand as both guardians and targets. Unseen adversaries covet their digital assets.

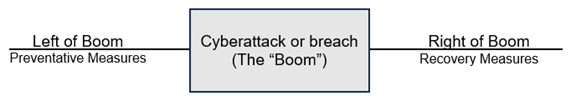
To navigate this treacherous terrain takes a two-pronged approach. Businesses must arm themselves with a sophisticated arsenal of cybersecurity strategies. On one side, the vigilant guards of prevention (Left of Boom). On the other, the resilient bulwarks of recovery (Right of Boom).

Together, these strategies form the linchpin of a comprehensive defense. They help ensure that businesses can repel attacks. And also rise stronger from the ashes if breached.

In this blog post, we’ll explain how to organize your cybersecurity approach into Left and Right of Boom.

What Do “Left of Boom” and “Right of Boom” Mean?

In the realm of cybersecurity, “Left of Boom” and “Right of Boom” are strategic terms. They delineate the proactive and reactive approaches to dealing with cyber threats

The Boom

“Left of Boom” refers to preemptive measures and preventative strategies. These are things implemented to safeguard against potential security breaches. It encompasses actions aimed at preventing cyber incidents before they occur.

“Right of Boom” pertains to the post-breach recovery strategies. Companies use these after a security incident has taken place. This phase involves activities like incident response planning and data backup.

Together, these terms form a comprehensive cybersecurity strategy. They cover both prevention and recovery aspects. The goal is to enhance an organization’s resilience against cyber threats.

Left of Boom: Prevention Strategies

User Education and Awareness

One of the foundational elements of Left of Boom is employee cybersecurity education. Regular training sessions can empower staff. They help them identify phishing emails. As well as recognize social engineering attempts and adopt secure online behaviors. An informed workforce becomes a strong line of defense against potential threats.

Employee training reduces the risk of falling for a phishing attack by 75%.

Robust Access Control and Authentication

Implementing strict access control measures reduces the risk of a breach. It helps ensure employees only have access to the tools necessary for their roles.

Access control tactics include:

  • Least privilege access
  • Multifactor authentication (MFA)
  • Contextual access
  • Single Sign-on (SSO) solutions

Regular Software Updates and Patch Management

Outdated software is a common vulnerability exploited by cybercriminals. Left of Boom strategies include ensuring all software is regularly updated. They should have the latest security patches. Automated patch management tools can streamline this process. They reduce the window of vulnerability.

Network Security and Firewalls

Firewalls act as the first line of defense against external threats. Install robust firewalls and intrusion detection/prevention systems. They can help track network traffic and identify suspicious activities. Additionally, they help block unauthorized access attempts. Secure network configurations are essential to prevent unauthorized access to sensitive data.

Regular Security Audits and Vulnerability Assessments

Conduct regular security audits and vulnerability assessments. This helps to identify potential weaknesses in your systems. By proactively addressing these vulnerabilities, organizations can reduce risk. They can reduce the chance of exploitation by cybercriminals.

Penetration testing can also simulate real-world cyber-attacks. This allows businesses to evaluate their security posture effectively.

Right of Boom: Recovery Strategies

Incident Response Plan

Having a well-defined incident response plan in place is crucial. This plan should outline the steps to take in the event of a security breach.

It should include things like:

  • Communication protocols
  • Containment procedures
  • Steps for recovery
  • IT contact numbers

Regularly test and update your incident response plan. This ensures it remains effective and relevant.

Data Backup and Disaster Recovery

Regularly backing up data is a vital component of Right of Boom. Another critical component is having a robust disaster recovery plan.

Automated backup systems can ensure that critical data is regularly backed up. As well as making sure it can be quickly restored in the event of a breach. A disaster recovery plan allows businesses to resume operations swiftly after an incident.

Forensic Analysis and Learning

After a security breach, conduct a thorough forensic analysis. It’s essential to understand the nature of the attack. As well as the extent of the damage, and the vulnerabilities exploited.

Learning from these incidents enables organizations to strengthen their security posture further. This makes it harder for similar attacks to succeed in the future.

Legal and Regulatory Compliance

Navigating the legal and regulatory landscape after a security breach is important. Organizations must follow data breach notification laws and regulations. Timely and transparent communication with affected parties is essential. It’s vital to maintaining trust and credibility.

Get Help with a Strong 2-pronged Cybersecurity Strategy

Using Left and Right of Boom strategies can improve your security stance. These terms help you consider both important aspects of a strong defense.

If you’d like some help getting started, give us a call today to schedule a chat.

—
Featured Image Credit

This Article has been Republished with Permission from The Technology Press.

Emerging Technology Dangers to Defend Against in 2024

Choose Wisely: What Smart Home Tech to Avoid?

In the age of smart living, our homes are becoming increasingly intelligent. They’re designed to cater to our every need. Smart gadgets are transforming how we turn on the lights, home security, and more. They even help us feed our pets from afar.

But with the rapid evolution of this technology, it’s crucial to make informed choices. To know what to adopt and what to avoid. Every smart technology isn’t as helpful as another.

You also must be careful of things like security and oversharing. Some devices will spread your data far and wide without your realization.

Here are some tips on what smart home tech to adopt and to avoid.

Tips to Make Better Smart Home Device Choices

Adopt: Smart Lighting Systems

Smart lighting systems have proven to be both energy-efficient and convenient. They allow you to control the ambiance of your home. As well as schedule lights to go on and off. You can even change colors to match your mood.

These systems offer seamless integration with voice assistants. There are also many brands to choose from. Smart lights can enhance your home’s aesthetic and energy efficiency.

Avoid: Cheap, Unbranded Smart Devices

There is a definite allure to low-cost smart devices. Yet these unbranded alternatives often compromise on security and functionality. You have to ask yourself, “Why are they so cheap?”

They may also be selling your data. And who reads those long user acceptance policies? You risk a lot by choosing a cheaper, unbranded device.

Investing in reputable brands ensures several benefits. Including:

  • Regular updates
  • Security patches
  • Compatibility with other smart home devices
  • Long-term support

Cutting corners on unknown brands may end up being costly. This is true for both security and performance.

Adopt: Smart Thermostats

Smart thermostats, like Nest and ecobee, learn your habits. They adjust your home’s temperature accordingly. They contribute significantly to energy savings. They do this by optimizing heating and cooling based on occupancy patterns.

There is also the convenience of using smartphone apps and voice control. These devices offer convenient climate management while reducing utility bills.

Avoid: Overcomplicating Security Systems

Robust security systems are essential. But overcomplicating them with unnecessary gadgets may lead to confusion and inefficiency. The more devices you add to a security system, the more exposure for your network.

Focus on key elements like smart locks, security cameras, and motion sensors. Opt for systems that offer user-friendly interfaces. Look for straightforward operation. You want to ensure effective home security without unnecessary complexities.

Adopt: Smart Home Hubs

Smart home hubs are popular. Brands such as Amazon Echo and Google Nest Hub serve as the central smart command centers. They give you one place to manage all your smart devices.

These hubs enable seamless communication between various devices. As well as simplify control through voice commands or smartphone apps. Investing in a compatible hub ensures a harmonious smart home experience.

Avoid: Ignoring Privacy Concerns

The convenience of smart home tech should not come at the expense of your privacy. Be cautious about devices that constantly record audio or video. Especially if done without clear user consent. Regularly review privacy settings. Limit data collection. Choose devices from reputable companies that focus on user privacy and data security.

Be sure to watch for announcements about changes. For example, Amazon recently opted users in automatically to Amazon Sidewalk. This is a shared neighborhood Wi-Fi. Unless you were aware, you may have known to opt out if you wanted.

Adopt: Smart Home Security Cameras

Smart security cameras provide real-time monitoring and remote access. They also enhance the safety of your home. Look for cameras with features like motion detection, two-way audio, and cloud storage.

Many brands offer reliable, user-friendly security camera systems. These help you keep an eye on your property and keep your family safe.

Avoid: Impulse Buying Without Research

The excitement of new gadgets can lead to impulse purchases. Before buying any smart home device, conduct thorough research. Read reviews and compare features. Also, assess compatibility with your existing devices.

Take the time to check out a device before buying. This helps ensure that you make informed decisions tailored to your smart home’s needs.

Keep Your Smart Home Efficient & Secure

Smart home technology is rapidly multiplying. Our homes now look like something from Back to the Future II or The Jetsons. A well-informed choice today can pave the way for a smarter and safer home tomorrow.

We’d love to help you keep your smart home efficient and secure. Give us a call today to schedule a chat.

—
Featured Image Credit

This Article has been Republished with Permission from The Technology Press.